Check a vendor's email security, domain age and headers before you sign
Before a supplier gets access to your systems, a quick public check catches obvious gaps: no DMARC policy, a permissive SPF record, a domain registered last month, missing security headers. DomainDNA returns all of these for each vendor domain in one JSON answer.
How IT vendor management teams use DomainDNA API
- List the vendor domains under review.
- Call /api/report for each (or /api/email-security for five at a time).
- Flag DMARC none or missing, SPF ending in +all or ?all, a very young domain, and a low security-header score.
- Attach the JSON to the vendor file and ask the supplier about each flag.
DomainDNA reads only public information: the public homepage, public DNS over HTTPS and the registry's RDAP record. It is a first-pass signal, not a full security assessment.
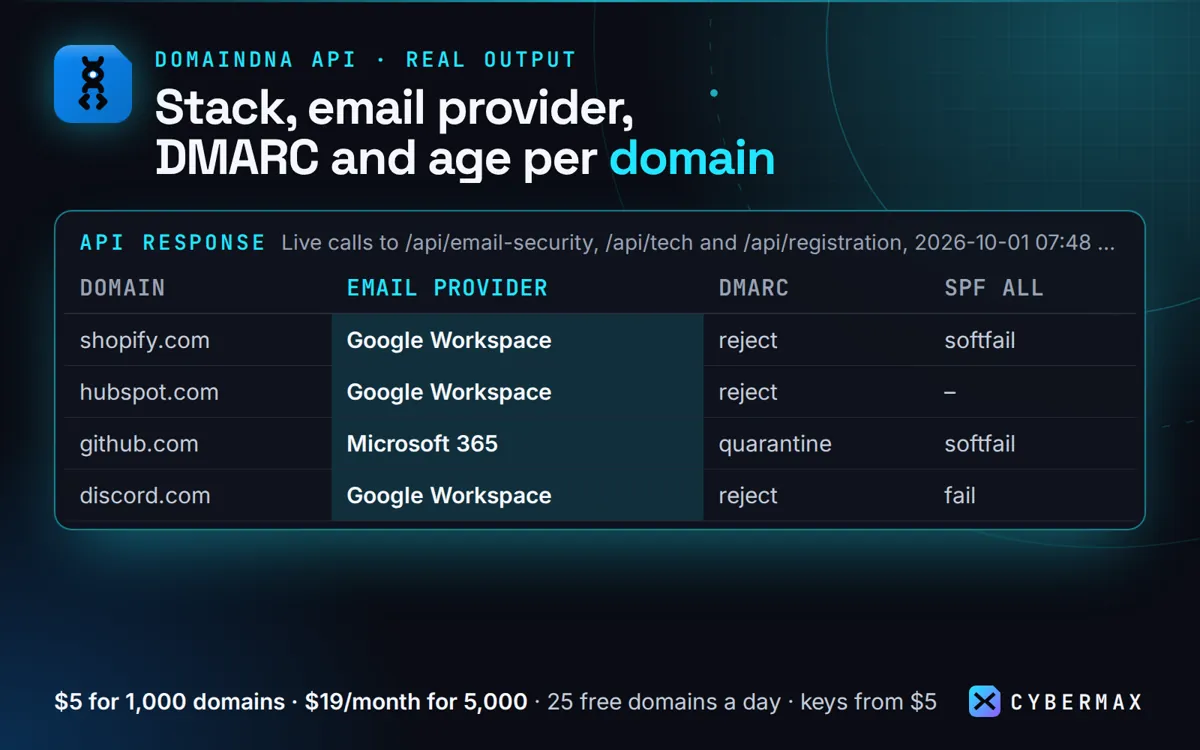
Live calls to /api/email-security, /api/tech and /api/registration, 1 Oct 2026
| Domain | Email provider | DMARC | SPF all | Age | Tech (first 3) |
|---|---|---|---|---|---|
| shopify.com | Google Workspace | reject | softfail | 21.6 y | Shopify, Tailwind CSS |
| hubspot.com | Google Workspace | reject | – | 21.6 y | HubSpot CMS, HubSpot, Cloudflare |
| github.com | Microsoft 365 | quarantine | softfail | 19.0 y | Contentful |
| discord.com | Google Workspace | reject | fail | 25.9 y | Webflow, Google Tag Manager, Google Fonts |
| wordpress.org | Other / self-hosted | reject | fail | 23.5 y | WordPress, Google Tag Manager, Google Fonts |
| zoom.us | Proofpoint | reject | softfail | – | Google Tag Manager, OneTrust |
Source: products/domaindna-api/store/listing.json (live API calls, 2026-10-01 07:48 UTC).
FAQ
Does it check TLS certificates?
Not in the API. The DomainDNA tool on Apify adds TLS expiry.
Why not a full security rating service?
Rating services add breach and port data on a yearly contract. DomainDNA is a cheap first pass: $5 for 1,000 domains or $19/month for 5,000.
DomainDNA API: full guide with prices and alternatives · All use cases · Store