A patch list every Monday: what attackers exploited this week
Free security newsletters tell you the stories. Kevscope Weekly gives your patch team the list: every vulnerability CISA added to its Known Exploited Vulnerabilities catalogue in the last 30 days with its due date, CVSS and EPSS score, a watchlist of new critical CVEs that are not in KEV yet, and the CSV files and build script behind every figure. Rebuilt every week from CISA KEV, FIRST EPSS and NVD.
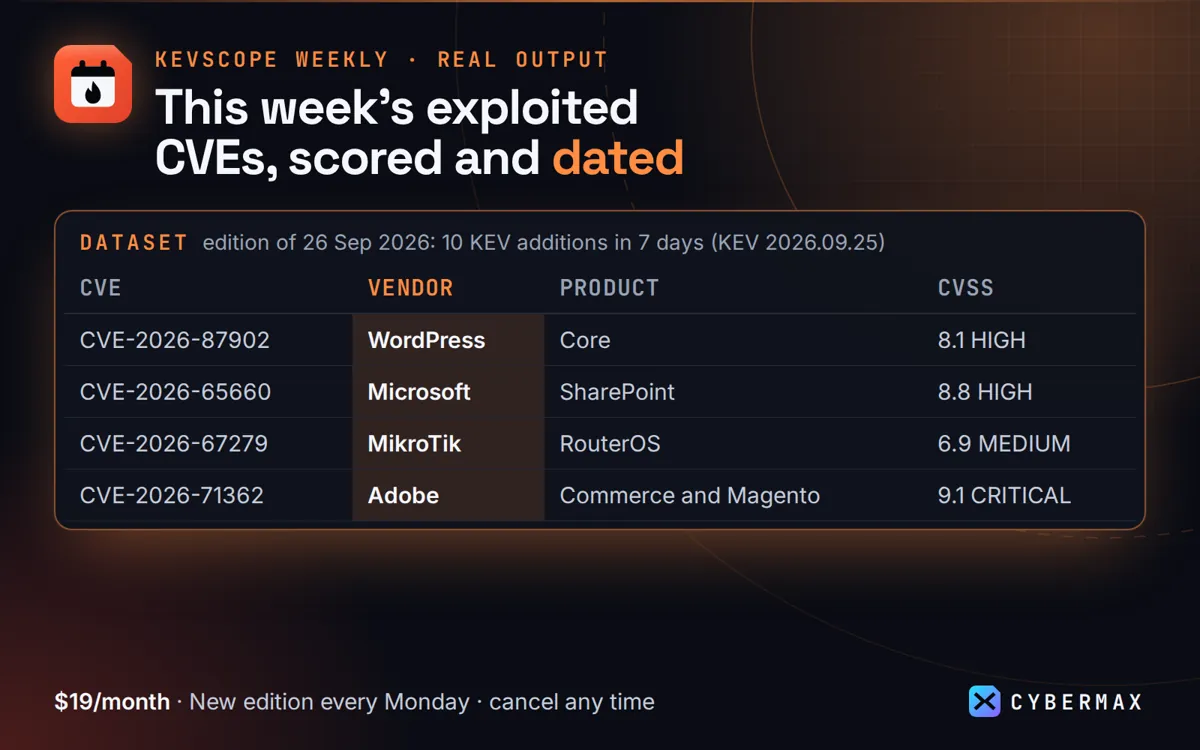
Newest KEV additions in the 26 Sep 2026 edition (KEV catalogue 2026.09.25, EPSS of 25 Sep)
| CVE | Vendor | Product | CVSS | EPSS | KEV due |
|---|---|---|---|---|---|
| CVE-2026-87902 | WordPress | Core | 8.1 HIGH | 2.88% | 2026-09-28 |
| CVE-2026-65660 | Microsoft | SharePoint | 8.8 HIGH | 1.22% | 2026-09-28 |
| CVE-2026-67279 | MikroTik | RouterOS | 6.9 MEDIUM | 0.71% | 2026-09-28 |
| CVE-2026-71362 | Adobe | Commerce and Magento | 9.1 CRITICAL | 89.62% | 2026-09-27 |
| CVE-2026-5430 | WSO2 | Multiple Products | 10.0 CRITICAL | 0.58% | 2026-09-27 |
| CVE-2026-93616 | Check Point | Multiple Products | 9.8 CRITICAL | 19.65% | 2026-09-25 |
Source: kev-added-last-30-days.csv from the 26 Sep 2026 edition (revenue/packs/polar/kev-weekly/release/kev-brief-weekly-latest.zip), built from CISA KEV 2026.09.25, FIRST EPSS of 2026-09-25 and NVD.
Kevscope Weekly vs the alternatives
Published prices, each checked on the date shown; prices change, so confirm on each site.
| Product | Price | Free | Checked |
|---|---|---|---|
| Kevscope Weekly | $9/month or $79/year | Live KEV data preview | live |
| SANS @RISK | Free (with free SANS membership), weekly email | yes | 2026-10-10 |
| Vulnerable U Premium | $49/month or $499/year | free newsletter | 2026-10-10 |
| PageCrawl.io (monitor the KEV page yourself) | Standard $160/year ($13.33/month); Enterprise $300/year | 6 pages, 220 checks a month | 2026-10-10 |
Why teams pick Kevscope Weekly
- A data product, not a news digest: each edition is a table you can hand to a patch team, with CISA due dates.
- In the 26 Sep 2026 edition, 195 KEV entries (11.3%) scored below 7.0 on CVSS: a HIGH-and-CRITICAL-only patch policy would skip them although each is known to be exploited.
- CSV files and the build script ship with every edition, so every number can be checked or re-run.
- $9/month, cancel any time; yearly $79.
How it works
- Subscribe and download this week's PDF and ZIP (HTML report, CSVs, build script).
- Sort kev-added-last-30-days.csv by KEV due date and hand it to the patch team.
- Check the critical watchlist for new CVEs with high EPSS that are not in KEV yet.
- Next Monday, the new edition replaces it.
FAQ
Why not SANS @RISK or another free newsletter?
Read them for the stories; they are good and free. Kevscope Weekly is structured data: KEV additions with due dates, EPSS and CVSS in CSV form, ready to load into a ticket queue or spreadsheet.
Why not just watch the CISA KEV page?
You can, for free. The brief adds EPSS and CVSS to each entry, a watchlist of critical CVEs not yet in KEV, trends, and the files, every week.
What sources are used?
CISA's Known Exploited Vulnerabilities catalogue (CC0), FIRST EPSS scores and NVD CVE records. Not affiliated with CISA, NIST, MITRE or FIRST.
Is it advice for my environment?
No. It is general information built from public data; your own asset inventory decides what to patch first.
Can I cancel?
Yes, any time; you keep the editions you downloaded.